Tag Archives: malicious traffic
Denial-of-Service Protection for Colocation: What Businesses Should Know
A denial-of-service attack can make a website, application, or network resource unavailable by overwhelming or disrupting the systems that legitimate users depend on. For businesses running critical infrastructure in a colocation environment, that makes DoS protection an important part of the broader network security conversation.
LightWave Networks provides colocation, network connectivity, monitoring, and managed networking services for businesses with a range of infrastructure needs. Understanding how denial-of-service attacks work can help organizations evaluate their risks and determine what protections they should discuss with their IT teams and colocation providers.
What Is Denial of Service?
Denial of service, commonly abbreviated as DoS, describes an attack intended to prevent legitimate users from accessing a network, system, application, or other resource.
An attacker may accomplish this by consuming available bandwidth, overwhelming a server with requests, exploiting how a network protocol handles traffic, or exhausting other resources needed to keep a service available.
A distributed denial-of-service attack, or DDoS attack, follows the same general objective but uses multiple systems to generate the attack traffic. The distributed nature of a DDoS attack can make malicious traffic more difficult to distinguish and block.
Whether an attack comes from one source or many, the primary target is availability.
How Does a Denial-of-Service Attack Work?
A denial-of-service attack works by creating more traffic, requests, or resource demand than the targeted system can effectively handle.
Consider a web server that can process a certain number of requests at one time. If malicious traffic consumes its available capacity, legitimate visitors may encounter slow responses, connection failures, or an unavailable service. This is one example of a denial-of-service attack, but attackers can also target network bandwidth, applications, or other infrastructure resources.
The result does not have to be a complete outage. A DoS (denial of service) incident may degrade performance enough to interfere with normal operations even when some users can still connect.
For a business, that disruption can affect websites, customer portals, internal applications, communication systems, or other services that depend on network availability.
What Are the Main Denial-of-Service Types?
Denial-of-service types vary according to the resource or layer being targeted.
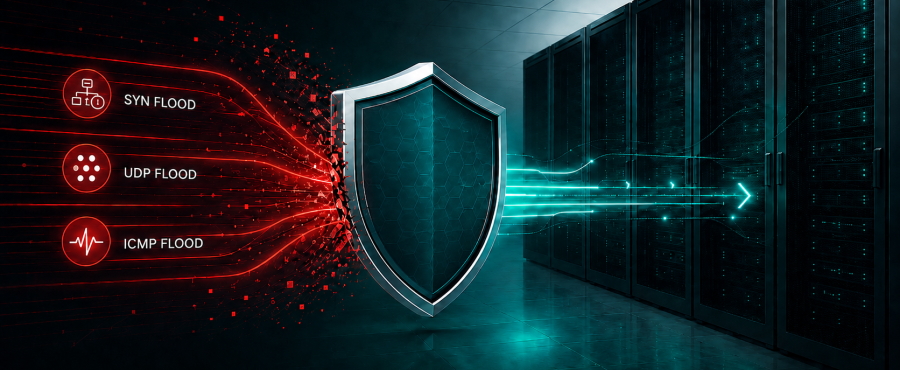
Volumetric attacks attempt to consume available bandwidth with large amounts of traffic. Protocol-based attacks can consume resources in network devices or servers by taking advantage of how certain protocols handle connections or requests. Application-layer attacks focus on applications or services, often by generating requests that require significant processing resources.
DDoS attacks can increase the scale of these techniques by directing traffic from numerous systems toward the same target.
Understanding the type of attack matters because there is no single denial-of-service solution that addresses every scenario. Effective protection depends on where the attack occurs, what resources it targets, and how the affected infrastructure is configured.
Why Does Denial-of-Service Protection Matter for Colocation?
Colocation moves business-owned servers and networking equipment into a professionally operated data center, but the customer still has an important role in protecting the systems running on that hardware.
Physical data center security cannot prevent every network-based attack. A server can remain safely locked in a cabinet with redundant power and cooling while still becoming unreachable because malicious traffic is consuming network or system resources.
That is why businesses evaluating colocation should consider both the facility and the network supporting it.
Network capacity, connectivity, monitoring, routing, firewall management, and access to technical support can all influence how an organization prepares for and responds to availability threats.
LightWave Networks’ colocation services include network connectivity through an IPv4 and IPv6-enabled, fully redundant BGP network. LightWave also provides 24/7 network monitoring and dedicated bandwidth options as part of its broader infrastructure services.
What Can Denial-of-Service Protection Include?
Denial-of-service protection is usually layered because attacks can target different resources in different ways.
Depending on the environment and threat, defensive measures may include traffic monitoring, firewall rules, filtering, rate limiting, routing changes, upstream provider coordination, capacity planning, and controls designed to identify or reduce suspicious traffic.
Some providers may describe these capabilities as denial-of-service programs, denial-of-service mitigation, DDoS mitigation, or related network security services. The terminology matters less than understanding exactly what the protection covers.
Businesses should determine where traffic is monitored, what happens when abnormal activity is detected, who is responsible for responding, and whether additional providers or services are involved in mitigation.
Denial-of-Service Prevention and Mitigation Are Different
It is useful to distinguish denial-of-service prevention from denial-of-service mitigation.
Prevention focuses on reducing vulnerabilities and making infrastructure less susceptible to disruption. This can include secure configuration, software updates, disabling unnecessary services, appropriate firewall controls, capacity planning, and ongoing monitoring.
Mitigation focuses on reducing the effect of an attack that is already occurring. Depending on the attack and network architecture, denial-of-service mitigation may involve filtering traffic, limiting certain requests, changing routes, blocking malicious sources, or coordinating with upstream network providers.
No denial-of-service prevention strategy can guarantee that an organization will never experience an attack. The goal is to reduce exposure, improve resilience, and establish a response plan before a disruption occurs.
What Should You Ask a Colocation Provider About DoS Risks?
DoS planning should happen before an attack rather than during one.
When evaluating a colocation provider, ask how the network is monitored and what happens when unusual traffic patterns are detected. Find out what firewall, routing, and managed networking options are available and what responsibilities remain with your internal team.
It is also important to understand how the provider communicates during network incidents, whether it coordinates with upstream carriers when necessary, and what options may be available if your infrastructure becomes the target of unusually high traffic.
LightWave Networks offers managed network services that include network monitoring and management of firewalls and other network components. Businesses with specific DoS concerns should discuss their architecture and requirements directly with the provider rather than assuming a particular level of protection is automatically included with colocation.
Build DoS Planning Into Your Colocation Strategy
Denial-of-service attacks target availability, which makes them especially important for organizations that depend on continuous access to websites, applications, and network services.
A strong colocation strategy should consider more than physical space, power, and cooling. Network architecture, monitoring, connectivity, security responsibilities, and incident response can all affect how resilient your infrastructure is when abnormal or malicious traffic appears.
LightWave Networks provides colocation and network infrastructure services designed around individual business requirements. Reach out to LightWave Networks to discuss your denial-of-service concerns, current infrastructure, and the protections you may need in a colocation environment.
SOURCE: